Vulnerabilities · 2024 · Humansignal
CVE-2024-26152
Humansignal Label Studio vulnerability
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 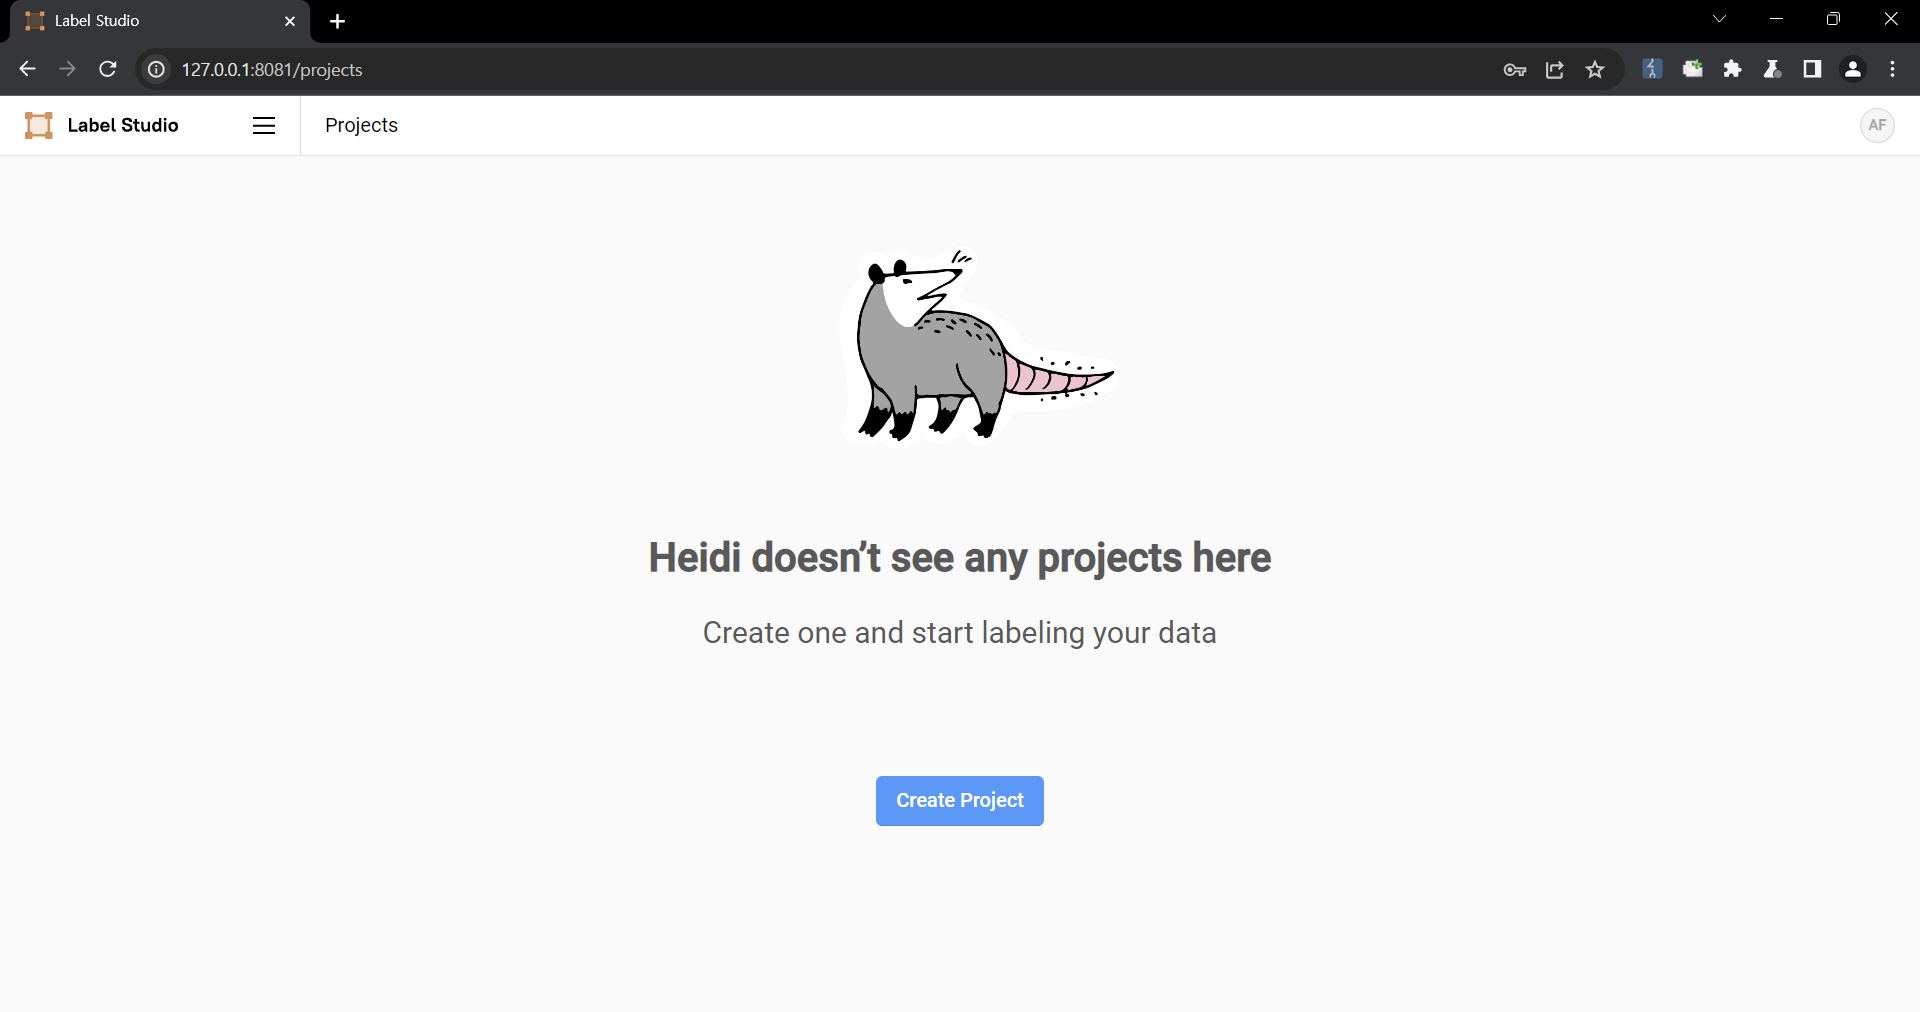 2. Upload a file containing the payload using the "Upload Files" function. 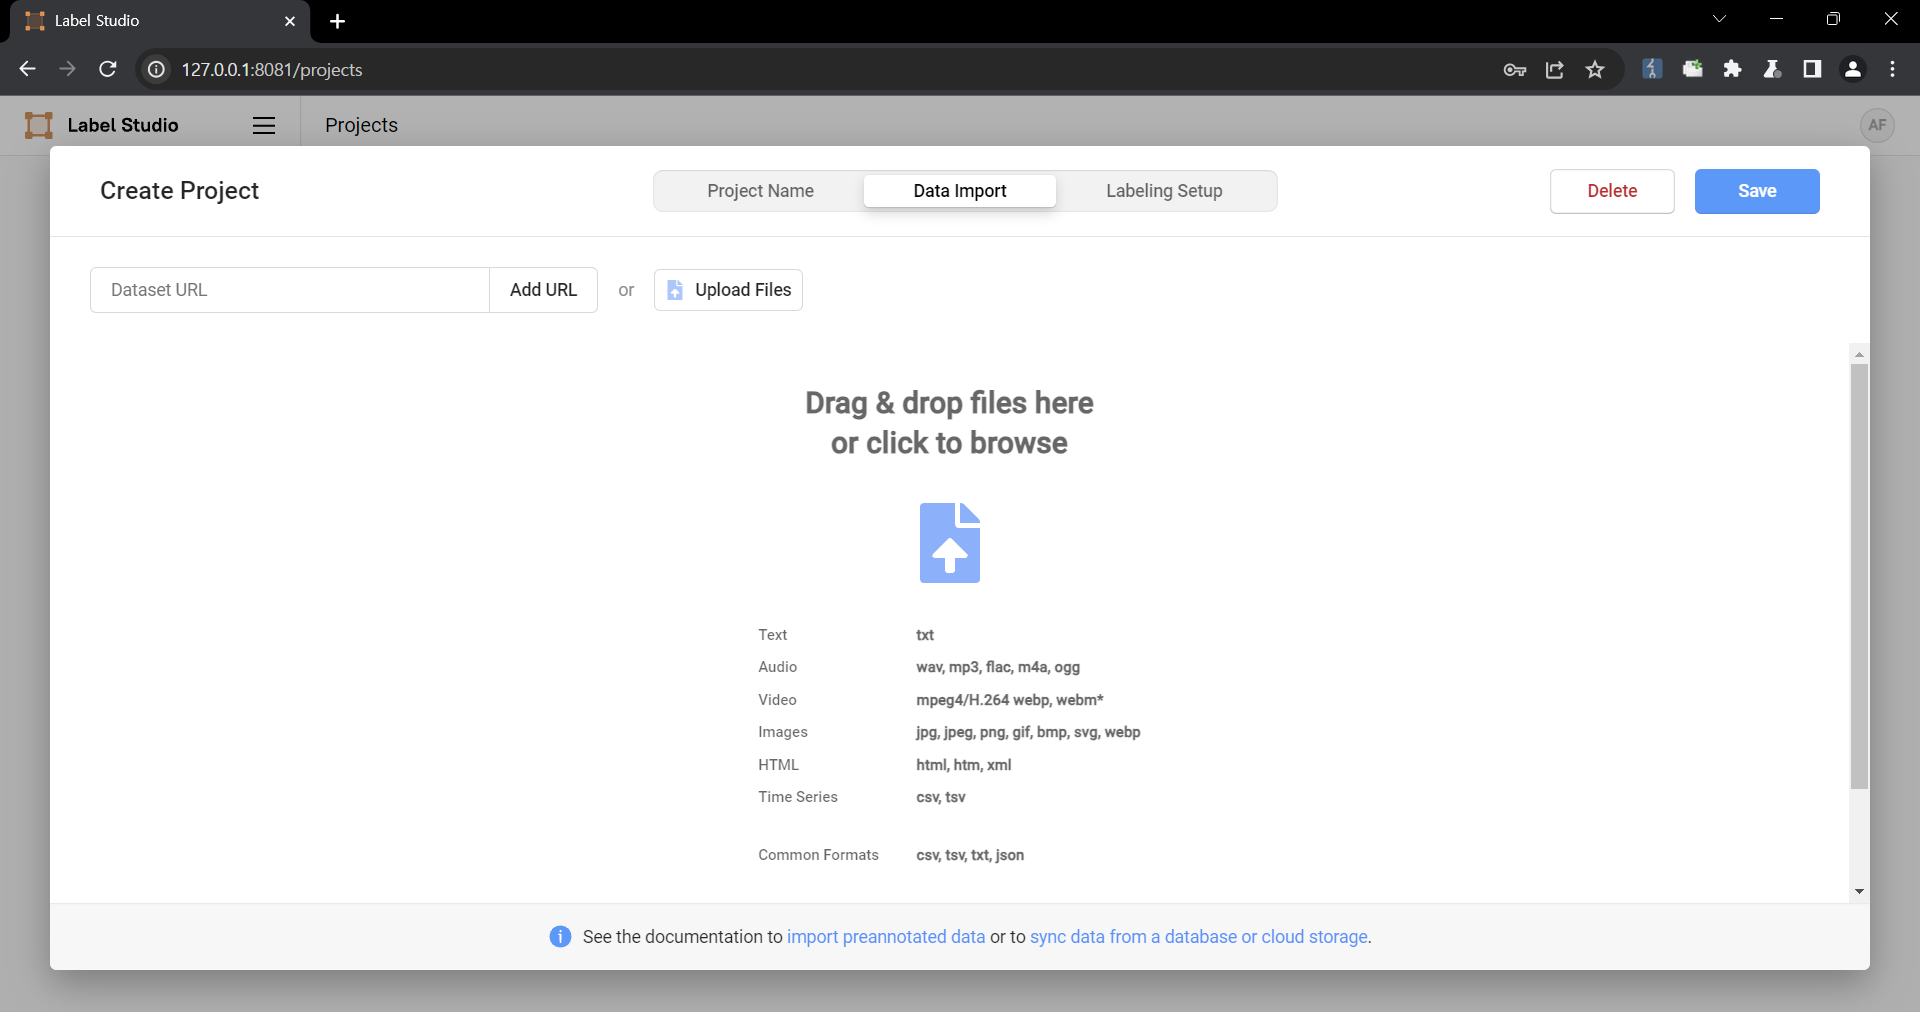 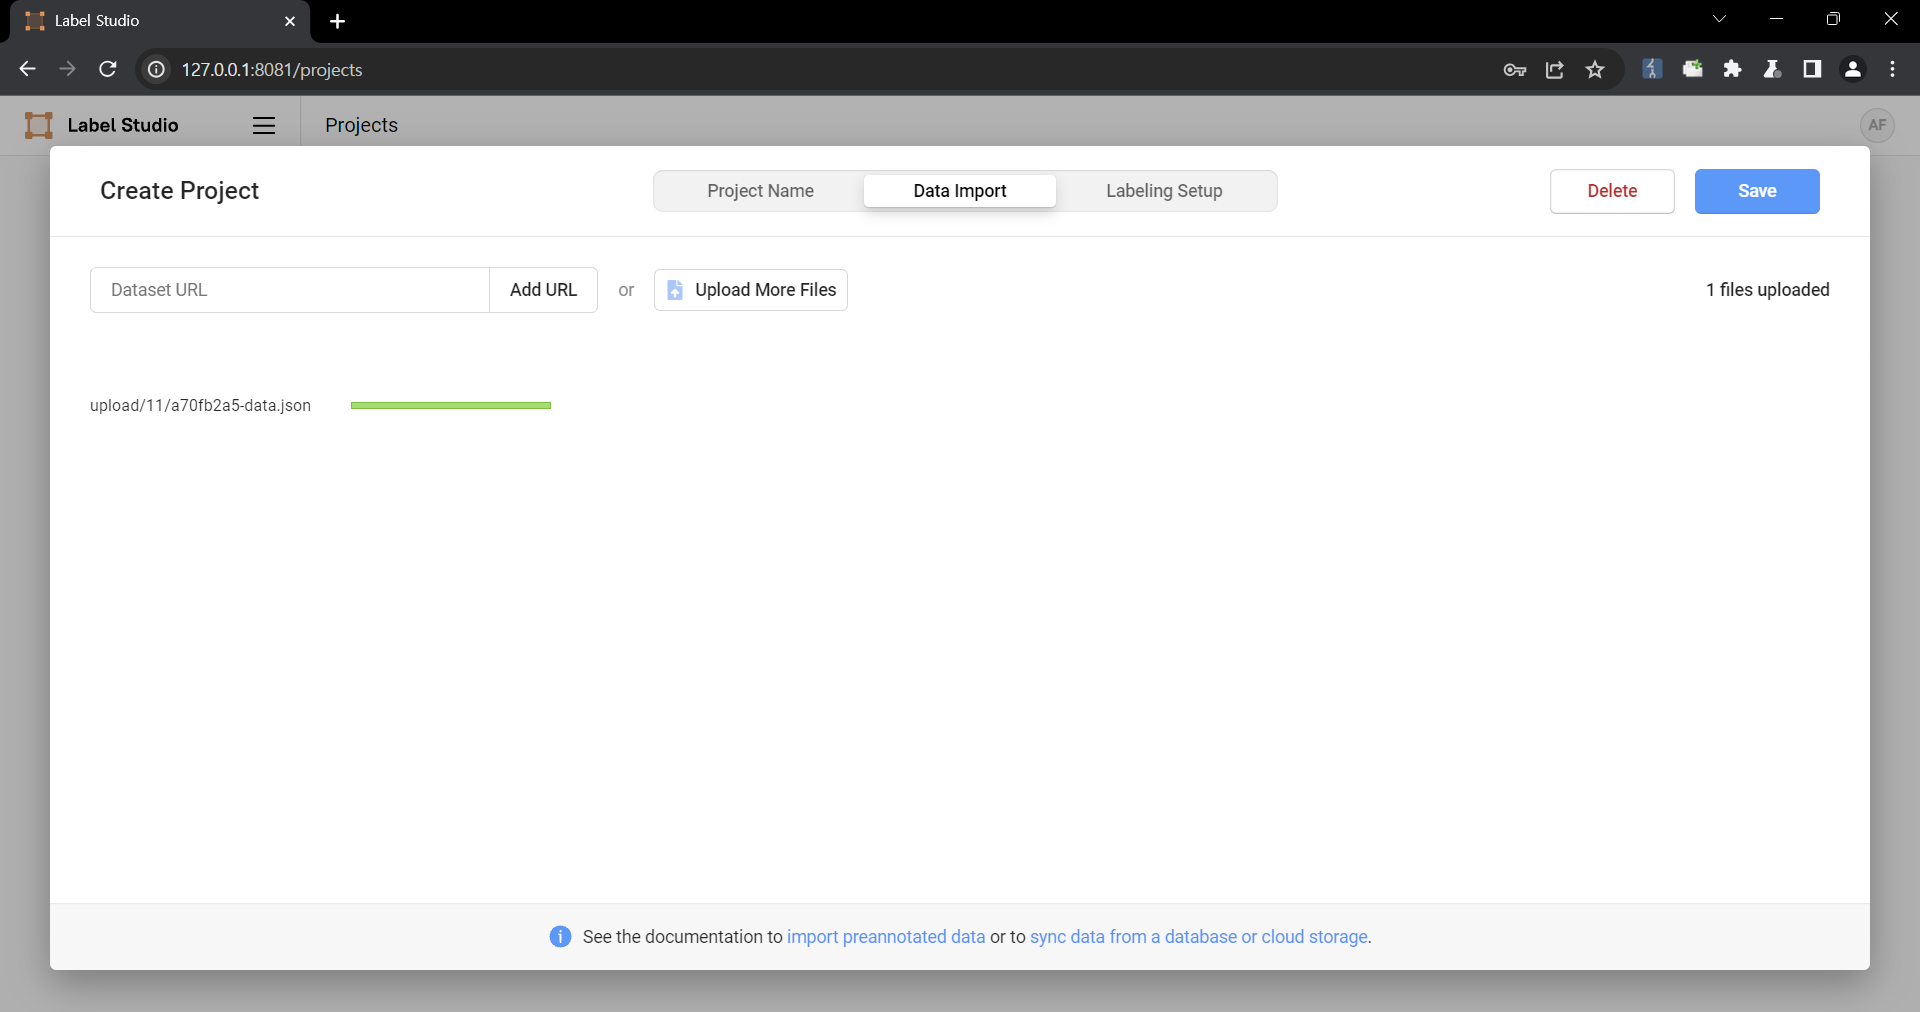 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>" } ] } } ``` 3. Select the text-to-image generation labeling template of Ranking and scoring 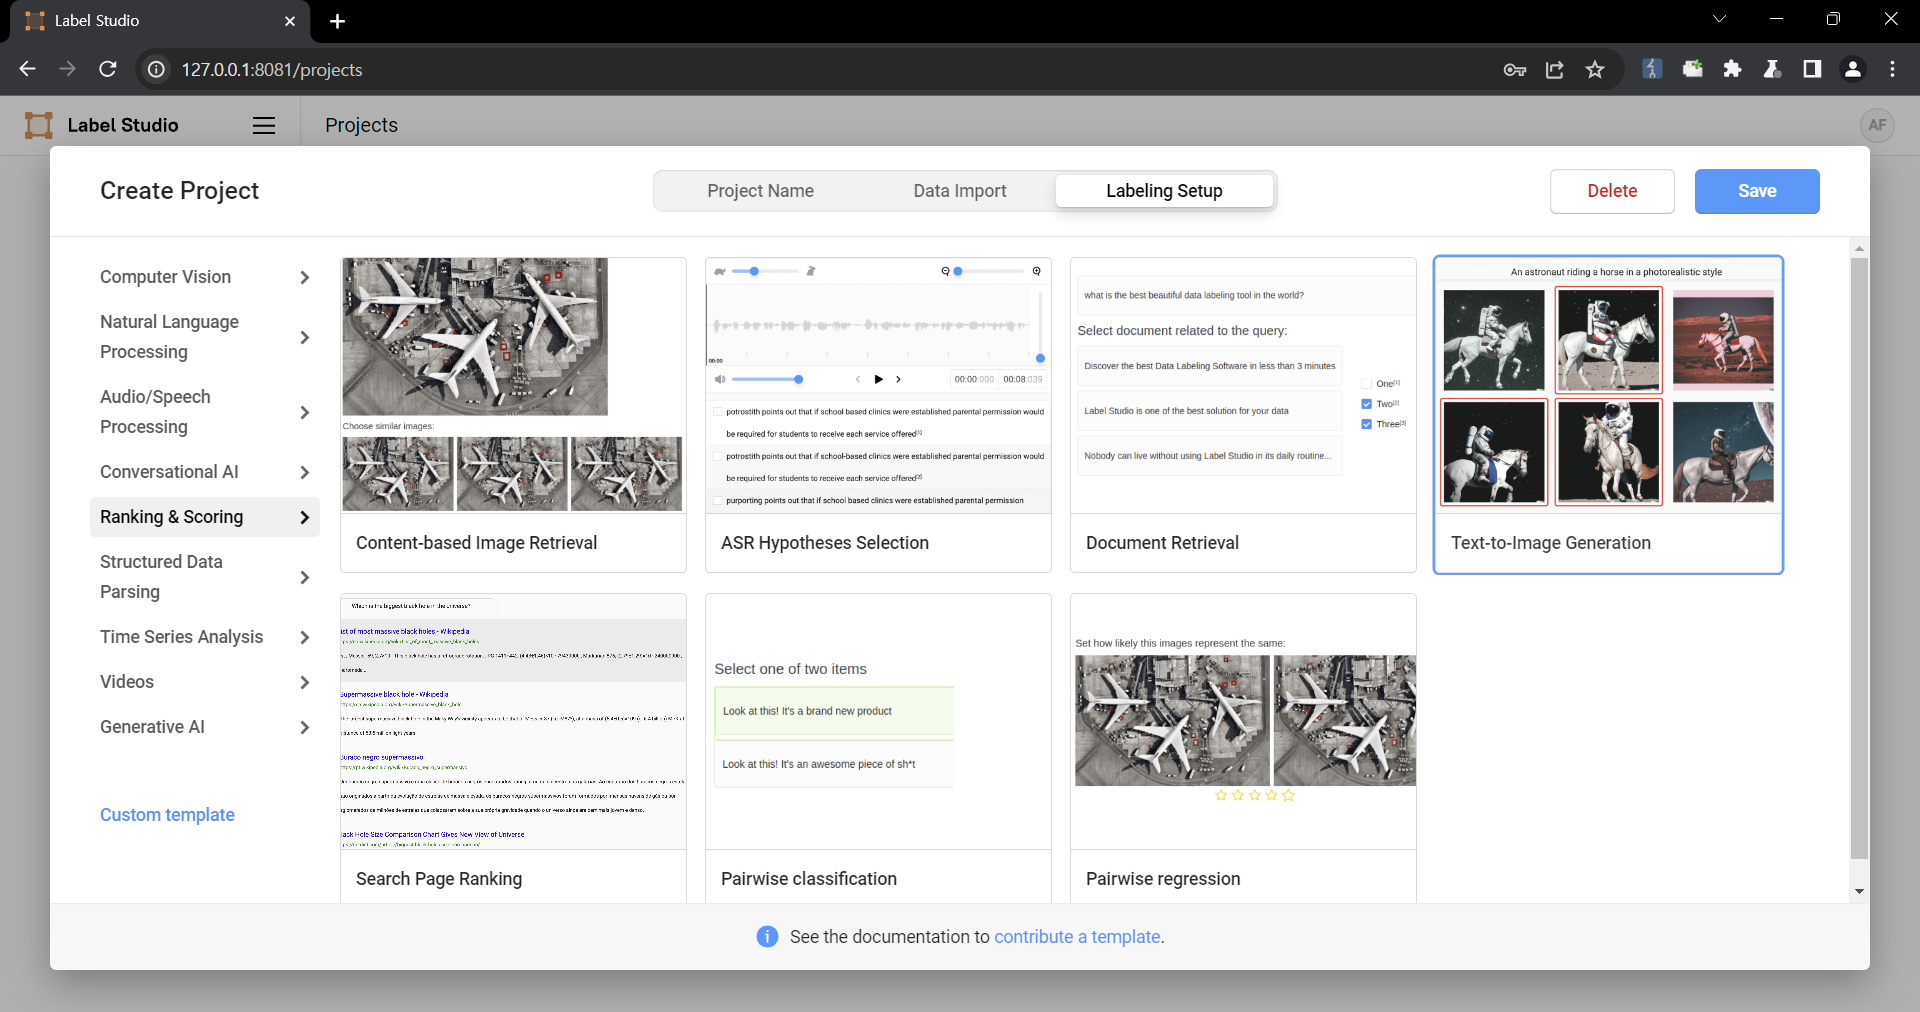 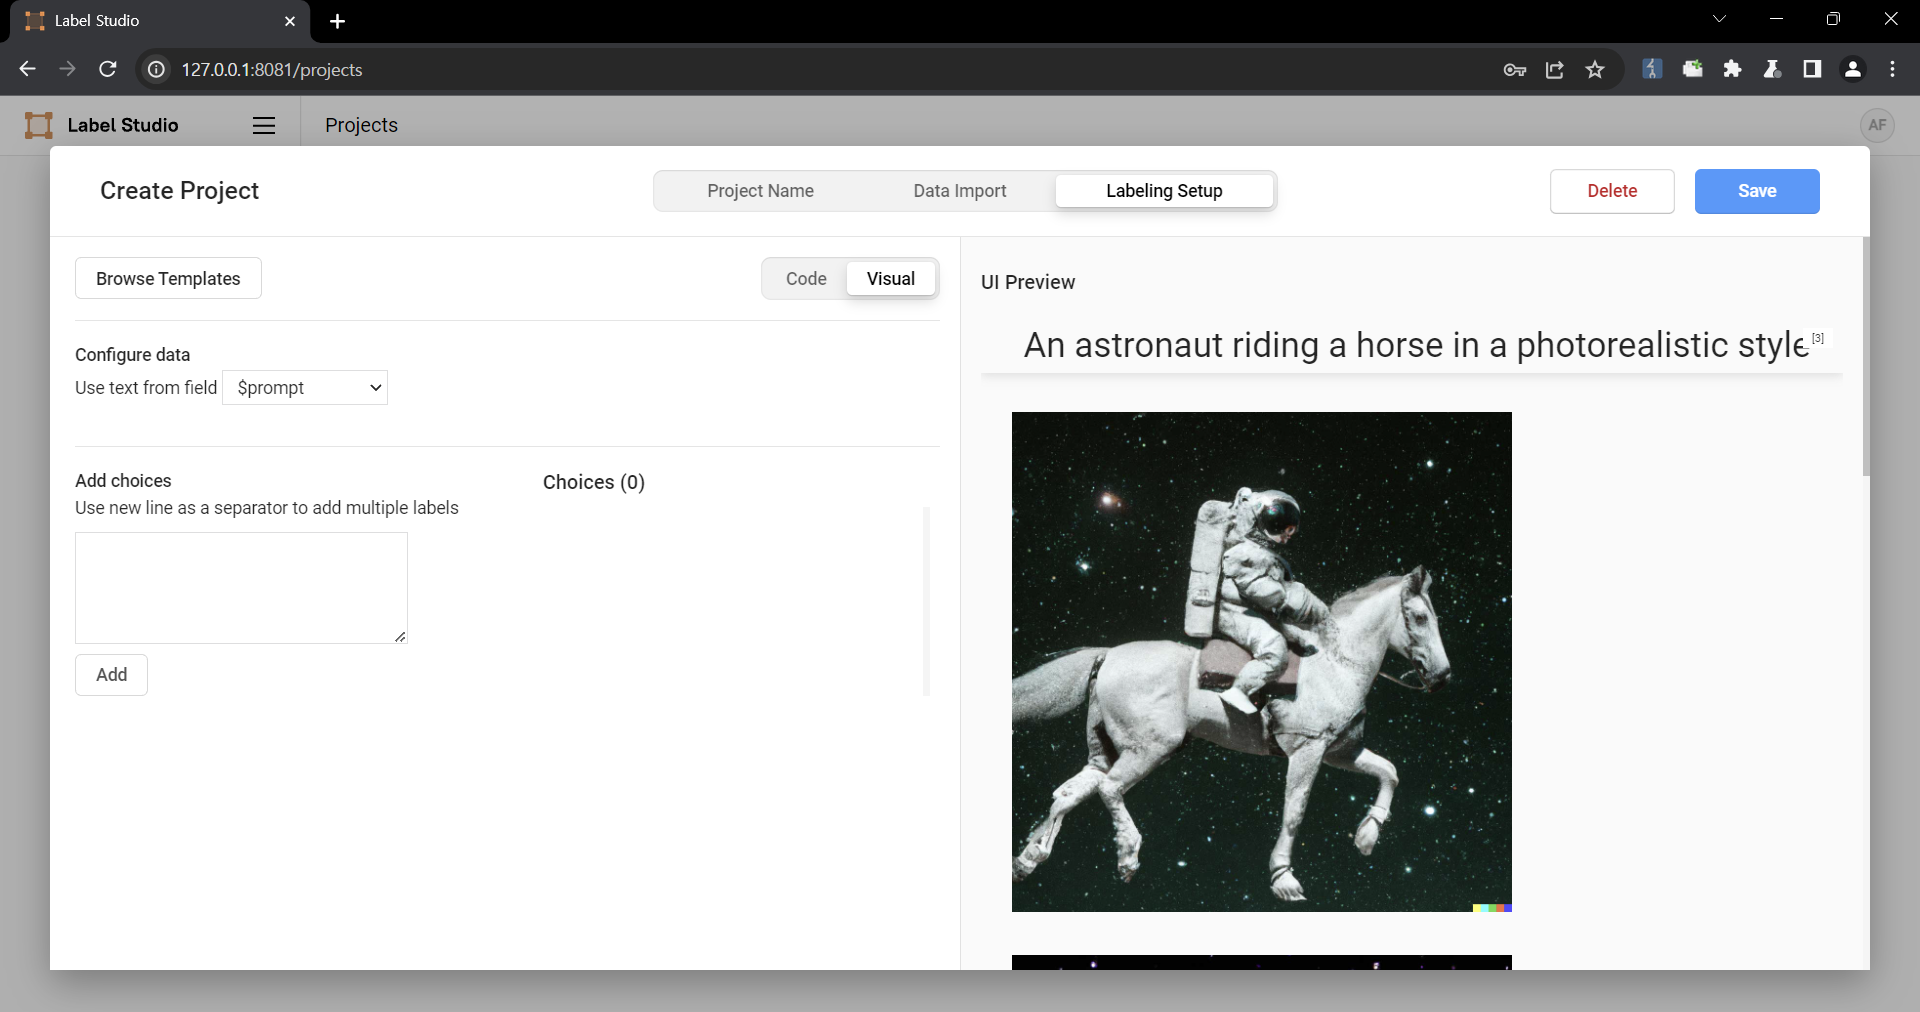 4. Select a task 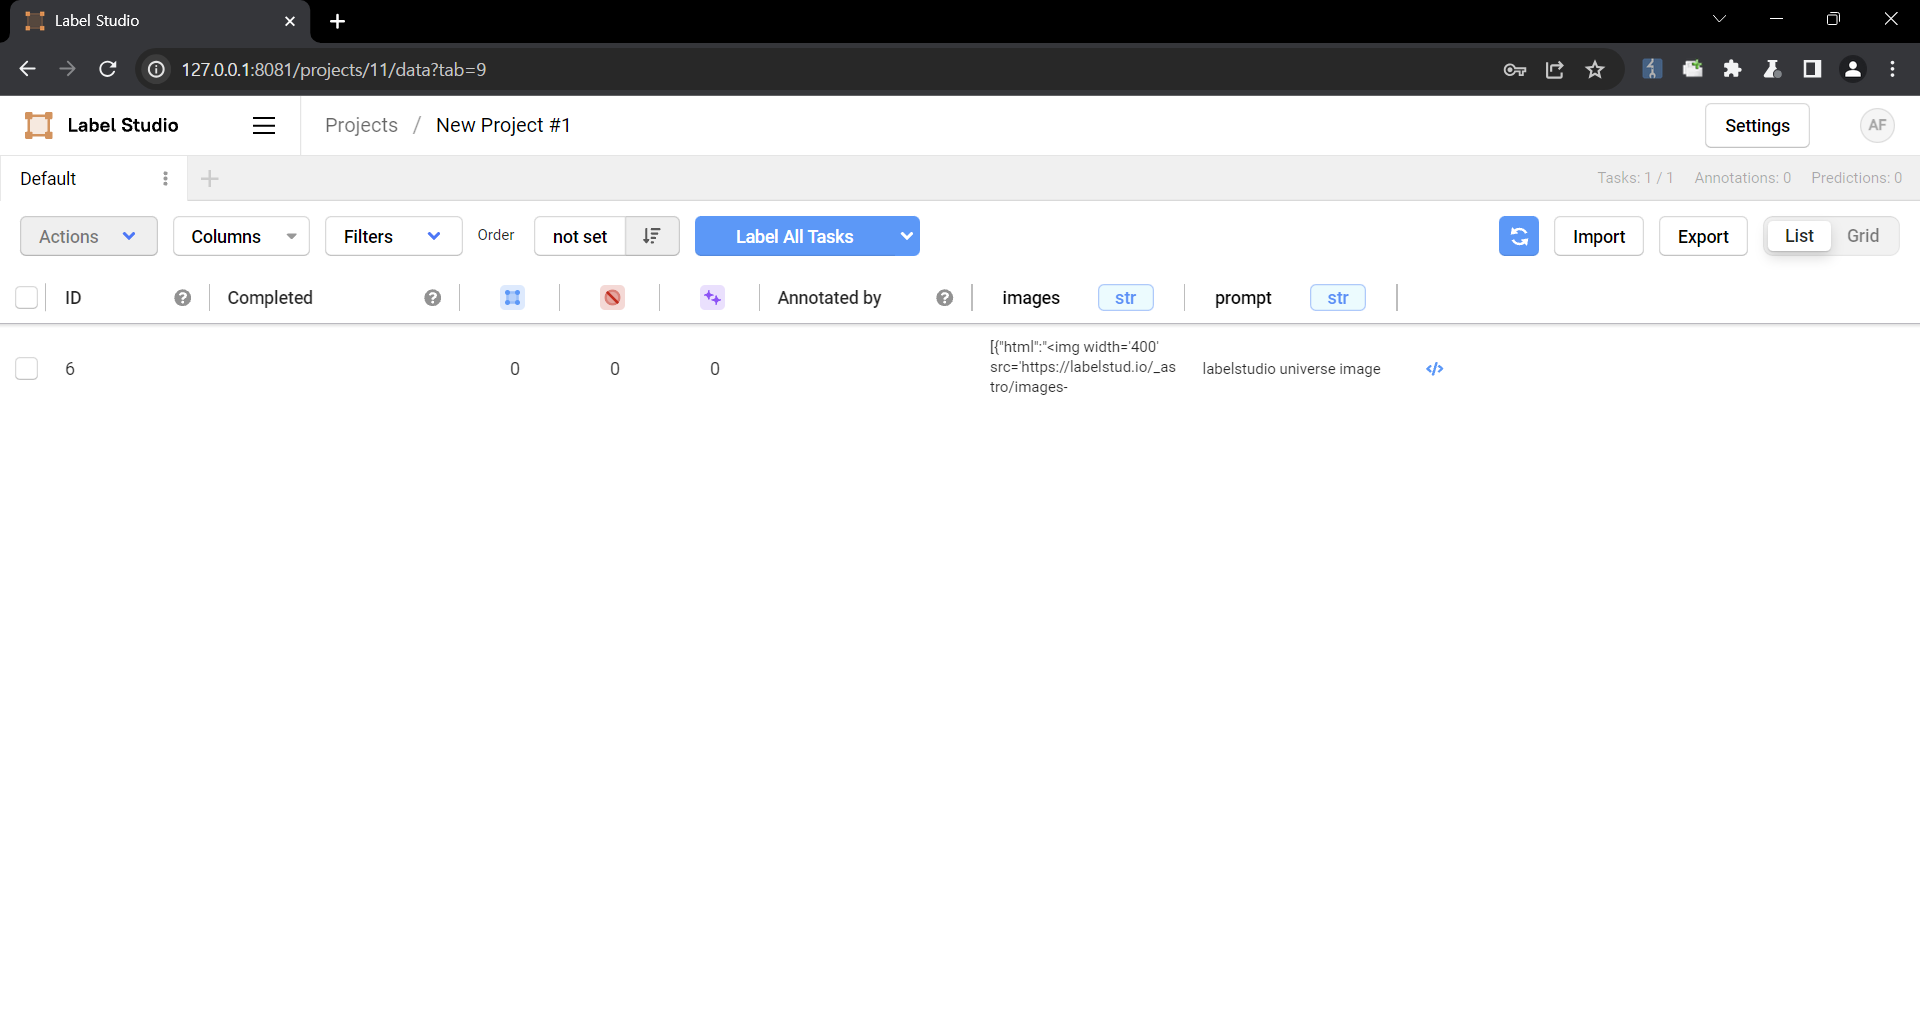 5. Check that the script is running 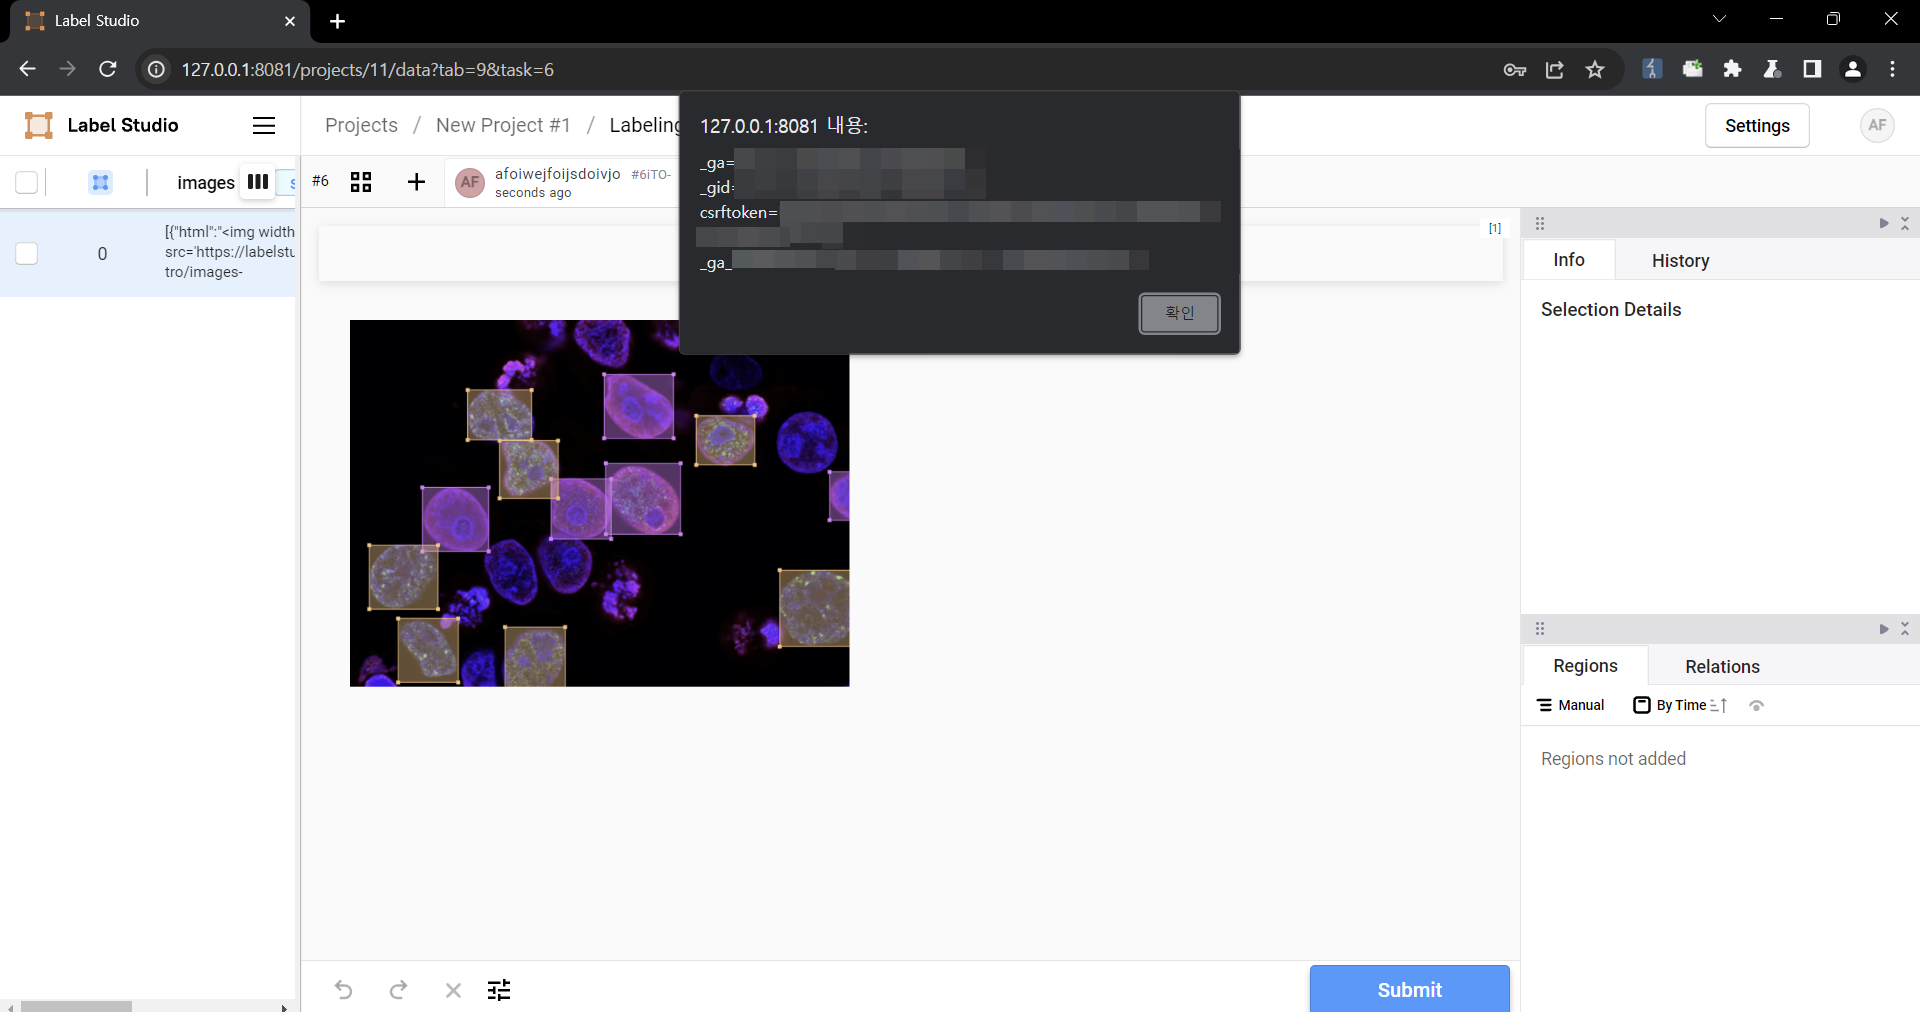 ### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Affected products
Label Studio. The exact versions are in the references.
What to do now
- Check your exposureFind out whether Humansignal Label Studio runs anywhere in your environment, including systems of suppliers.
- UpdateInstall the version in which the vendor fixed the vulnerability. The references lead to the advisory.
- Limit access until thenIf you cannot update at once, take the system off the internet or restrict who can reach it.
References
- github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg · Exploit
- github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8 · Patch
- github.com/HumanSignal/label-studio/pull/5232 · Patch
- github.com/HumanSignal/label-studio/releases/tag/1.11.0
- nvd.nist.gov/vuln/detail/CVE-2024-26152
- github.com/pypa/advisory-database/tree/main/vulns/label-studio/PYSEC-2024-249.yaml
- github.com/advisories/GHSA-6xv9-957j-qfhg
- nvd.nist.gov/vuln/detail/CVE-2024-26152
- cve.org/CVERecord?id=CVE-2024-26152
More vulnerabilities in Humansignal products
Data: CVE list and the NVD. This product uses data from the NVD API but is not endorsed or certified by the NVD.